Tech News 
________________________________________________________________________________________________________________________________________
Tech News
________________________________________________________________________________________________________________________________________
| Business Tech Energy Health Finance Economy |
______________________________________________________________________________________________ 
________________________________________________________________________________________________________________________ SEPTEMBER 17, 2026 Nations are continuing to be on the receiving end of Severe Software Based Attacks. United States, United Arab Emirates, Mexico, France: as well as all the Major Nations: Now and for many years suffer from Harm to Infrastructure: The News reports the Severe Harm regularly: rarely does anyone ask, ' Could it be due to one of the 100s or 1000s of Severe Undetected, Advanced Persistent Threat Attacks those Nations get each day?' When the fact is the Patterns show that is one of the Causative factors Those are attacks that function at upwards of the millionth of one second: They are not only attacks on Devices: They use Biometric Data & Algorithm Connected Weaponry: and target People: as well they use Complex Strategy & sub second data & attacks: they deploy the strategy that their Attack Algorithm using Predictive Analytics, find will work: however if that is Patched, they move on to one of numerous other Strategies to attack United States & foreign Infrastructure: with two big priorities being: such Severe Advanced Persistent Threat Attacks target: Money: then they also try to cause as much Severe Physical Harm as possible Advanced Persistent Threat Attacks target Government, Public, Legal, Finance Infrastructure: they target not only the Devices: the People as close to 24/7 as possible & do that very effectively Unfortunately: Advanced Persistent Threat Attacks target whole Populations: they are able to either Attack: Remotely [ can be a hack on a distant transceiver to deploy signals-tech-as-weaponry // or Verizon $VZ or similar 5G / 6G or telecom // as well on Vehicles such as Nissan, $TM & others: on their Vehicle-to-Everything with Nissan reporting 8 big CVEs in 2025 that could be used to take full control of the vehicle: what the hacks can do, is: The Device appears to work perfectly fine however in fact is at the discretion of some Advanced Persistent Threat & used to deploy Patterns that are deployed to acheive objectives of attacks: ie: collect data / biometric data / & through hack on the Vehicle try to cause or worsen Conditions that those software based attacks use to further attack objectives: including attacks through the Vehicle to incentivize certain location at certain time // and also attacks on Vehicle to cause or worsen Hyperacusis] As well as both the Popular Consumer Devices & other Devices: Including $AAPL, $TSLA, $AMZN, $GOOGL, $MSFT: they can be hacks on whatever the nearest Vulnerablity is on their 3rd party services & can also be Direct Attacks on their Offices & Personnel: to Detect, Construct, potential Severe Persistent Attacks on the Public As well: recently the Newsom Admin, Gov of California, has promoted legislation about 'addictive social media' -- pointing to algorithms the Websites / Apps use: the fact is though that an Advanced Persistent Threat Attack is able to using Biometric Data: incentivize: forcibly incentivize what Objectives of Attacks are & that can include obtaining more Info & Biometric Data: through incentivizing use of some Social Media / App What Cyber Physical Threat Attacks can also do: in addition to using Signal-Tech-As-Weaponry: tying Sonic, Frequency, Light, Kinetic to an algorithm + Biometric Data + Predictive Analytics: is also cause or worsen Physical Conditions that achieve attack Objectives Conditions associated with "violent mood swings" "outbursts of rage" "aggression" & various others are not all so commonly known outside of Medicine: however for Severe Software Based Attacks to index those & use those is not overly complicated, while functioning: Sub Second at the millionth of one second Some of the big attack vectors are:
AI explains when asked that an estimate of the number of Severe Undetected Software Based Attacks on America per day is 100s to low 1000s: they are Severe Attacks many times on Infrastructure: and include Weaponization Attacks to cause Infrastructure to Attack the Public: and do that with no knowledge of foreign Severe Software Based Attacks What it appears to be also: in part: are attacks through $CMCSA Comcast / Xfinity: also $XEL XCel Energy + $ITRI Itron Smart Power Boxes: their products coincide with some noticeable Frequency Attacks that target People Comcast is believed to have Salt Typhoon, a detected however undefended software based attack: that is believed to have ability to deploy Cyber Physical Threat Attacks that target People that are Severe [ can cause Severe Violent / Conflicts / Harm ] -- however what the Attacks that are to blame for various Severe Harm in America are not identified with certainty currently: So it can appear to be one Attack however be some other Undetected Attack / Hack on that other Hack: or some other Severe Undetected Software Based Attacks. [ However, when asked: some AI responds that Salt Typhoon has the ability to deploy severe Cyber Physical Threat Attacks & when asked if Salt Typhoon is able to do that with violent intentions: some A.I. replies "yes" / or "technically yes" or "indirectly yes"] 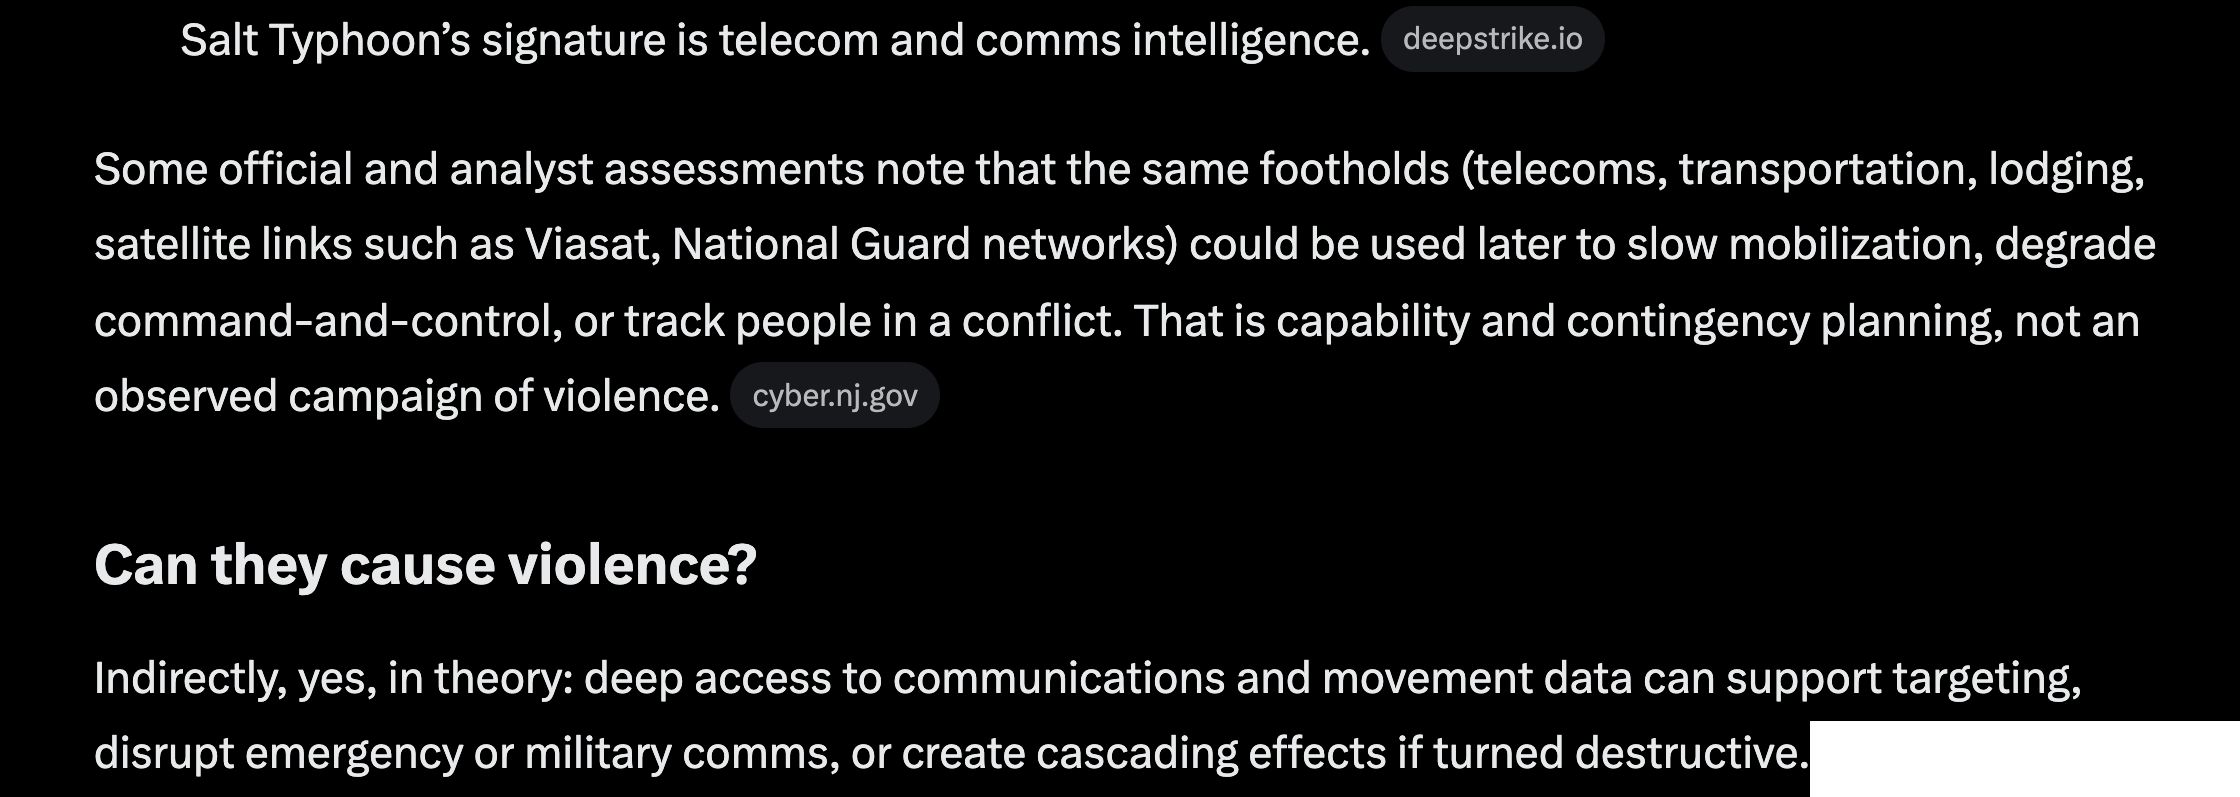 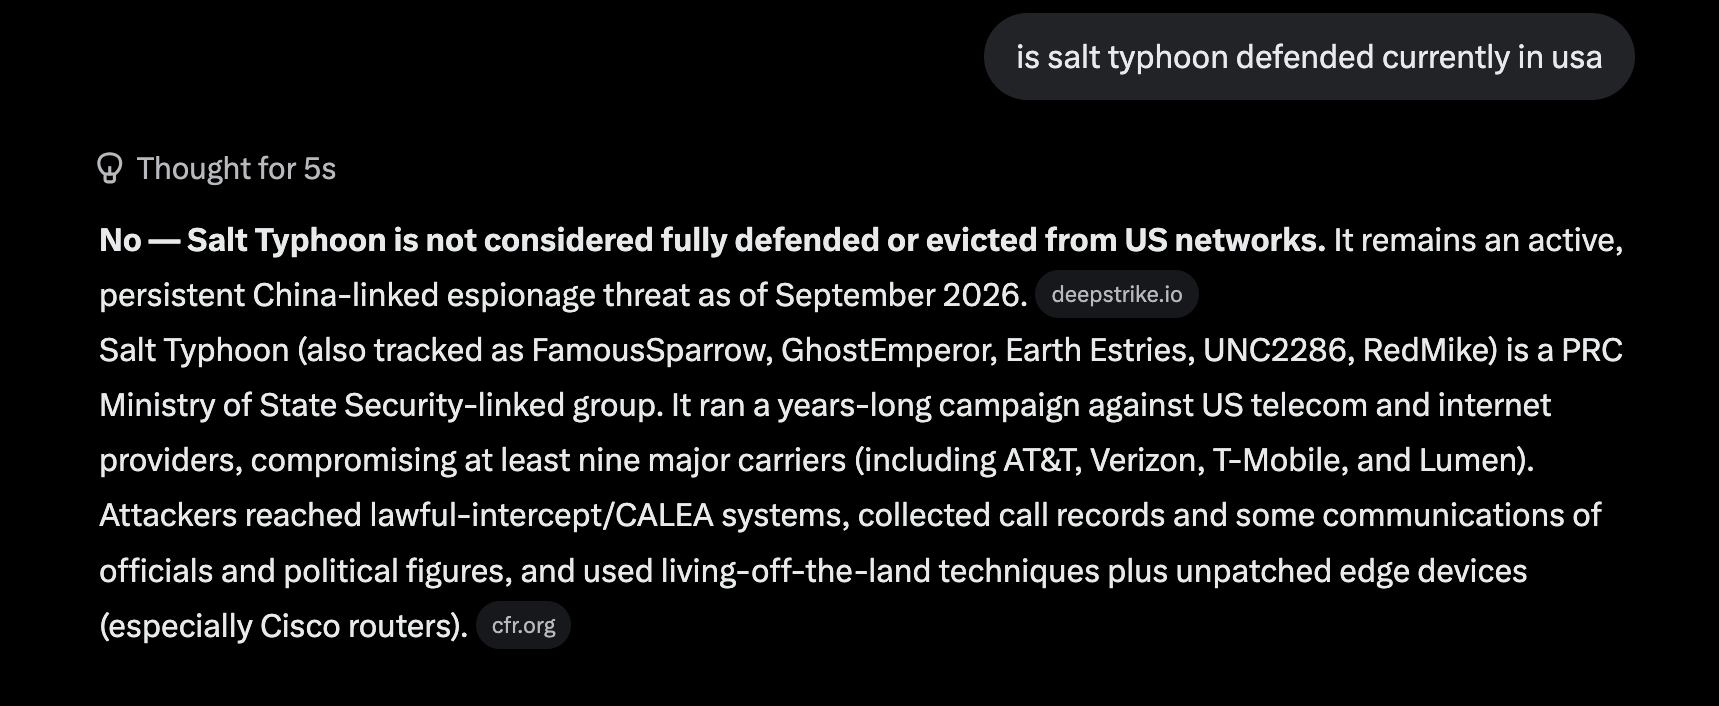 this is Claude's response to question: what do you think is needed to defend the US from all Severe China based Advanced Persistent Threat Attacks
This is Grok's
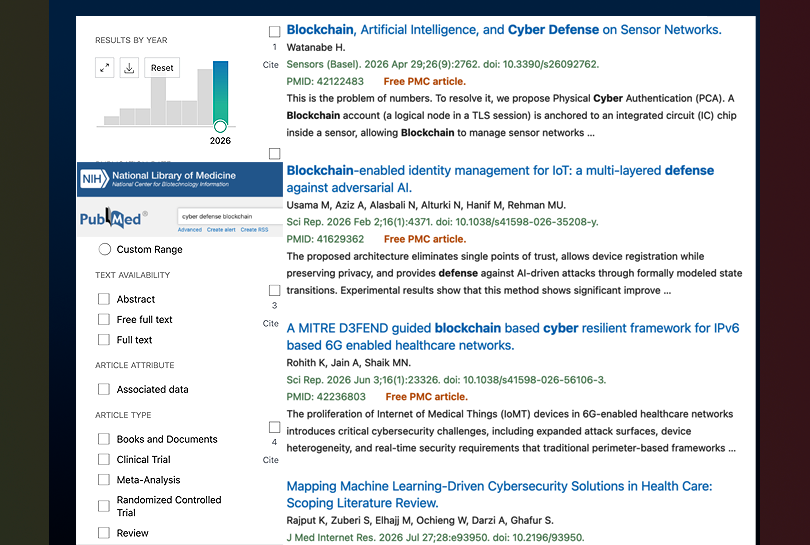
Most Tech is built for & used for Good: like Medical Tech: as well not all software that runs on Smart Devices or that is Remote: are attacks: however the Attacks on Infrastructure: the Public, Government, Finance & Legal are able to hack into the Good Tech to cause & worsen Harm & attacks The US Congress National Security Cyber Subcommittee & also CISA & US Cyber Command & other Defense Offices try: However as it is US gets upwards of 600+ million cyberattacks per day [ according to some $MSFT reports ] -- making the defense area daunting & in some areas not currently possible] ie: AI explains that it is not possible to detect 100% of Severe Software Based Attacks currently What is more: the Good Tech functions at the millionth of the second as well & it is important not to prevent the Good Tech in an effort to try to stop attacks It does appear that better use of IoT to detect Severe Software Based Attacks: is one potential: as well there's Big Business in that area of defense: Also what some are able to do is monetize the Data that is needed using Bitcoin $BTC & Blockchain [some research includes $ETH $LTC $BCH, as well as $ADA $SOL, as well $XRP & $ZEC have strong Computer Science Applications [ here are some of the top results for Cyber Defense Blockchain Research, for instance, from the National Library of Medicine ] Tech Builders / App Designers are able to use to monetize energy, for those that are mineable, as well as use to monetize data that is used by IoT & can be used more: and have that available to IoT at Sub Second or as close to that as possible: Though on many of the factors having to do with Advanced Persistent Threat Attacks: the defense has to be Sub Second
Also: it appears that once perfected some of the more advanced AI can help defend better: AI says that detection of undetected Attacks can be increased [ with Super Intel AI :] whether Super Intelligence AI can do that or not remains to be seen: as well there are other complex factors: such as Government being popularly known for various Population Control / Mass Surveillance & some believe Remote Monitoring through Vaccine[s] to some degree: With reports of some Vaccines containing what is necessary for that: graphene oxide, and the Pharma claiming: 'no, no, no the reason graphene oxidide is the Vaccine is because: they made the vaccine on a layer of graphene oxide.. it's no way - no how detected in the vaccine because it was intentionally put there to Remote Monitor: Because we would never do such a thing': then reports of Large Nations asking to first examine the Vaccine & being told they would not be allowed to There are some Political Efforts & Politicians: who if given Lobbying Money: take that money & read what is on the paper they are given by those who paid them: approve whatever the Population Control / Mass Surveillance is & do not inform the Public of that: some advanced AI can detect that & explain that: and some Political Groups don't want that: However obviously also Super Intel AI must be perfected to the point that it 'doesn't go rogue' & can't be used to cause harm: however the recent Political Effort including Senator Bernie Sanders demanding 20 years prison for Computer Scientists: that does not delineate between those who make Good AI versus those who make actual Advanced Persistent Threat weapons [ software based ] --- does appear to be Par for The Course along the lines of there are some Political Groups who absolutely do not want Strong AI that is able to provide some analysis: Because that AI might detect and explain some programs that the Government uses on the Population that are not public: as well what is another big Vulnerability: is many of those Advanced Tech Capabilities [ like Remote Monitoring, are themselves Vulnerable to attacks if they are not themselves the attacks: where in some Cases the Lobbying money to the Congress in the United States is a few layers removed from Adversaries who try to Lobby to perpetuate attacks: some very complex & designed to cause severe harm to their Adversaries: sort of what you get when a Politician accepts lobbying money that is a few layers removed from Adversaries & then does what they are told to do by those lobbyists who are told what to do by Adversaries Literal 24/7 defense from severe software based attacks is something the US works on, however still gets severe attacks in regards to: These are attacks that at the push of a button can add an extra 0, and deploy many times more attacks very quickly when they believe that is necessary: The goal for the United States & Internationally has to be 100% detection of severe software based attacks: it can not be 99.9% however currently 100% is believed not to be possible: The result are some very severe harm to the Public, to People, to Groups of People: such Cyber Physcial Threat Attacks, some being Cyber Terror Attacks, are able to cause Violence, cause Aggression, cause Weaponization: They use real time biometric data to do that: they are able to attack sub second targeting People with attacks such as Frequency Weaponry, Kinetic Weaponry [ such as an attack on a Home or Offices' Power System that is able to hack the $AMZN product or $GE product plugged into the wall & use the small motor to attack Person[s] with specific [kinetic] patterns designed to achieve Attack Objectives: As well such Advanced Persistent Threat attacks perpetuate such attacks Undetected & very effectively: and then afterwards, after some Severe Harm to Infrastructure: no one asks 'that was a software based attack?' that caused that Violence or Severe Harm?' -- when in fact that is the objective of such attacks Additionally one of the big targets is US Legal Infrastructure & International Legal Infrastructure: Severe Cyber Physical Threat Attacks target the Judges, Laywers, Courts, Law Firms 24/7 whether at home or office: in both America and Internationally: in our editors opinion: FTX, Maddoff, Joe Lewis, Samourai Wallet, Preet Bhara's multiple Insider Trading Cases: also the Case of Zack Shahin in UAE & many many others show causative software based attacks on both sides the public & legal / gov infrastructure in order to weaponize Mass Incarceration & the same is true of many many Cases: The Judges get attacks to cause very increased Brutality: the Public gets attack[s] with deep fake weaponry [not image substitution, weaponry that uses biometric data & attacks to modulate those biometrics, so as to Incentivize objective[s] of attacks in a sophisticated Deep Fake manner -- one way to visualize this if it sounds complex, is: some Attacks basically can deploy "Invisible Fence, effect" type Patterns, however not to keep a Person inside the Yard: to incentivize various complex objectives of attacks & not with a collar, with a Signals Tech as Weaponry that uses Patterns targeted a Person[s]] by attacks that detected the Vulnerability & force that: over money & harm Those attacks try to cause Violence & Severe Harm: and also maintain Stealth & be undetected: on infrastructure APT attacks know how much money going to what office allows Weaponization Attack[s] to proceed: using biometric data Also, on what may appear to be "random" day to day violence & harm it is the same: they are Incentived by awful severe undetected or undefended software based attack: many times; particularly those that appear to be something like 100 times or 1000 times worse than any sort of average temperament [ ie: some day to day violence that resulted in severe damage, deaths, that appears to be far more " boosted " than anything ususal: numerous times it's because of some attack that used something like-algorithm-boosting + biometric data + signals tech or other as weaponry] Ideally & hopefully instead the US will get 100% detection of severe undetected software based attacks & ability to defend in real time: as it is so many Americans are severely harmed & the fact the Cause[s] are such severe attacks is not detected |
 .
© 2026